{News}
by alchemain team


September 11, 2026……..the EU Cyber Resilience Act is in full effect. If you sell a product with digital elements into the EU and something in it gets actively exploited, the clock starts. 24 hours for an early warning. 72 hours for a full notification to your national CSIRT and ENISA. Then, once a fix exists, 14 days to file a final report proving it.
What's missing? The final report isn't due 14 days after you discover the flaw. It's due 14 days after you can have a reliable fix in production, and regulators expect that window to be short. So the real issue isn't "did we find it" but "can we get a fix out without breaking the product."
The Remediation Bottleneck
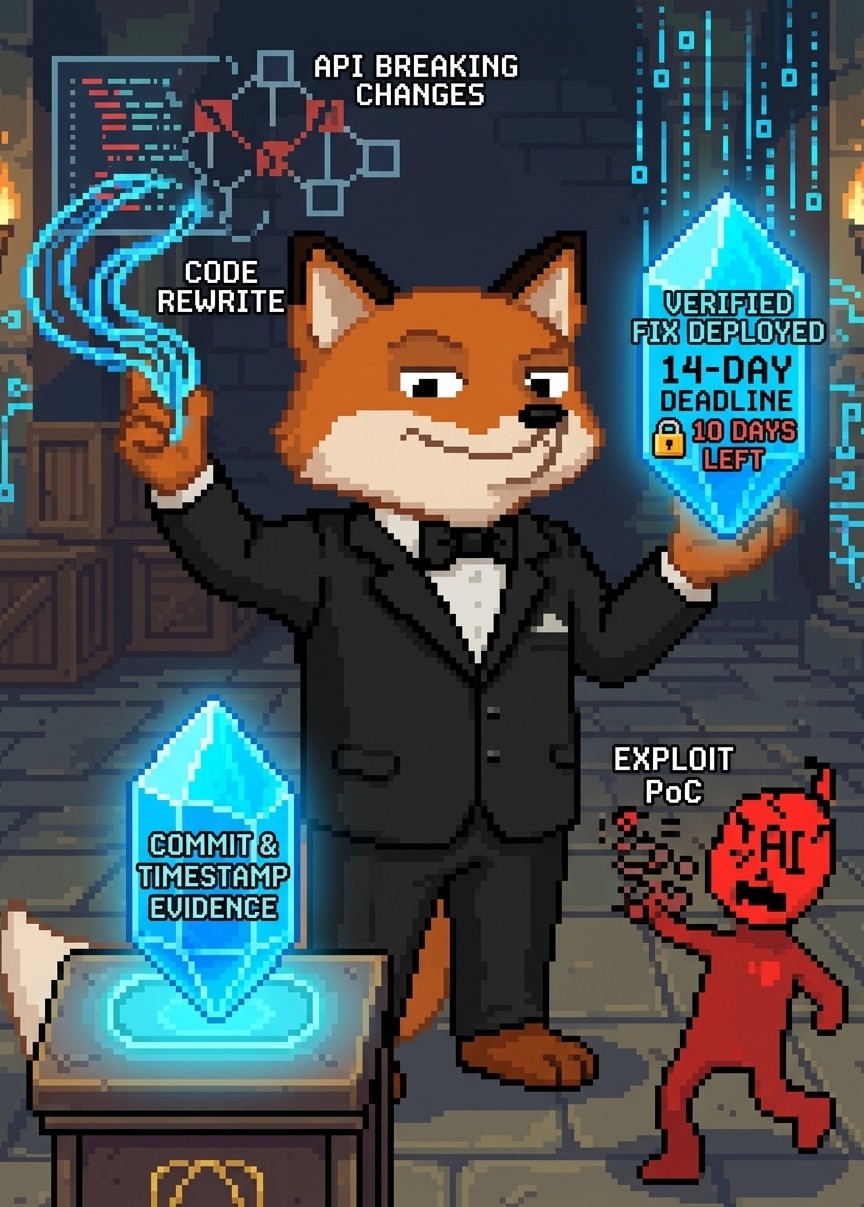
Dependency upgrades are a problem for many teams, and while they are still a pain for SCA tooling, a patched library very rarely drops in clean. It deprecates a method, kills an upcall default, renames a class. That's why even in the best of teams get buried by remediation work. You can have an accurate "safe" list and still miss the deadline, because it takes time to turn a CVE into a merged, tested fix.
The delay, between having a vulnerability and having a verified fix in production, is the real risk most organizations haven't accounted for yet. And it's about to get worse. CrowdStrike's 2026 Threat Hunting Report showed 88% of exploits with a public PoC went off within 48 hours of that PoC existing. Some state sponsored groups exploited the same flaw in 20 to 24 hours.
CrowdStrike admits: "AI allows attackers to scan and weaponize vulnerabilities at nearly the same pace as they are discovered." The regulators just legislated a fix window that was already generous by 2024 standards. By the time that deadline is in force, it may already be faster than the attacker.
Automated Fix Generation via 00felix
So a 14 day reporting deadline on top of a manual remediation process is a bad bet against regulators, and against the attacker. Which is exactly what 00felix is designed to address. 00felix already covers the detection piece. Continuous SCA and SAST scans across your entire fleet, with live security and vulnerability data from OSV, NVD, GitHub Advisory, and other datasets, plus an SBOM generated for every product and every release it produces, which conveniently happens to be the same artifact you're required to document under the CRA.
The part that actually counts for the attack and regulator deadlines is what happens after detection: When there is a real, certified-vulnerable package, 00felix pushes an upgrade to your build environment, applies rewrite code to fix breaking API changes the new version may require, tests the fix in your build pipeline to ensure the correct release of the patch, and produces a pull request, ready to merge. A human still reviews and approves it before anything ships, and it never runs on production systems. That's the level of evidence a notified body or CSIRT needs to justify a final report, and it lets a security team comply with Article 14 on time instead of scrambling at the last minute.
Future-Proofing for 2027
Another date to keep in mind is December 11, 2027, when the CRA's full scope kicks in: conformity assessment, CE marking, and the complete lifecycle record. Companies that treat September 2026 as a one-time incident will build the same record from scratch again 15 months from now, against threat actors who will be updating far faster by then than they are today.
The CRA assumes an enterprise can go from "we detect" to "we have a fix in production" at a pace regulators see as reasonable. AI is ensuring they'll have to accelerate that pace on both sides of the cycle. For most engineering teams locked inside dependency upgrade cycles that break something every time they update anything, that assumption isn't true today. Quietly filling that gap in your normal build process, without hiring additional headcount, is the part of CRA readiness worth solving before the next deadline hits and before the next exploit emerges.
If you'd like to see how 00felix can help you find and remediate your vulnerabilities at AI pace, click the "Book a Demo" button at the top of the page.